When a Police Officer's Flock Login Reached ICE
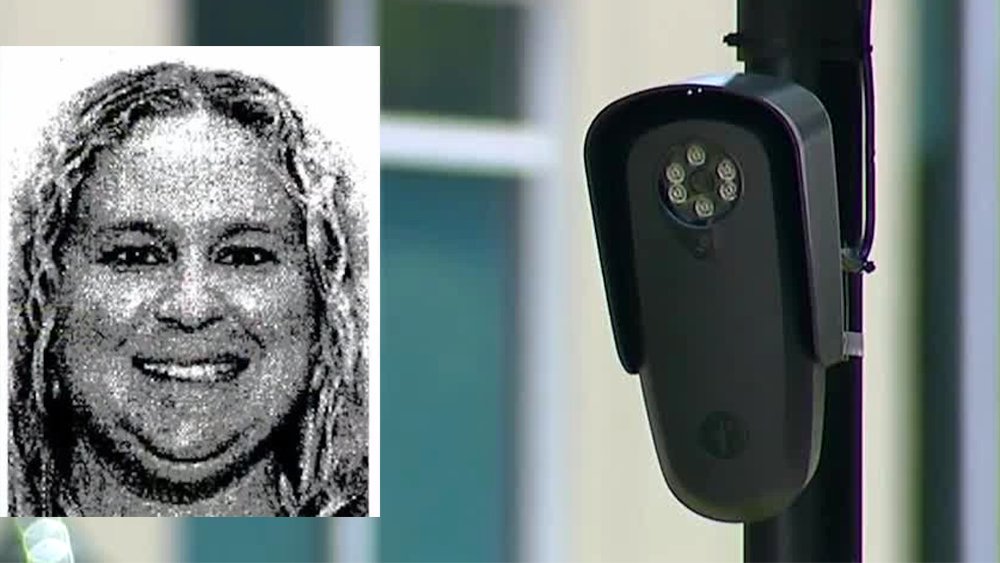
A Savannah police officer didn't hack into anything. She just gave her husband her login. Her husband, an ICE agent, then ran hundreds of searches through the department's Flock Safety license plate reader system, according to documents obtained by the U.S. Department of Homeland Security. No malware. No zero-day exploit. Just a password shared between spouses, and suddenly federal immigration enforcement had a direct line into local police surveillance infrastructure.
We tend to picture these systems as locked down. Authorized users only. Audit trails. Access controls. But the reality is messier. Flock cameras are already covering cities, building a searchable database of everywhere your car has been. But the credentials? They're treated like streaming service passwords, passed between shifts and shared with task force partners, sometimes handed to family members who happen to work for agencies with overlapping jurisdictions. When a local cop and an ICE agent are married, the line between "local policing" and "federal immigration enforcement" stops being a policy boundary and becomes a domestic arrangement.
This isn
Why Shared Logins Break Accountability
The most common reason teams share streaming or SaaS credentials is geography. Someone sees "Sorry, this content is not available in your region" and texts a coworker for their login. Within a week, that password lives in a Slack channel, a shared note, and three people's password managers. The account stops being a boundary and becomes a public utility.
This is where accountability dies. When the audit log records a query, it needs a user ID to attribute the action to a human. Shared credentials collapse five distinct identities into one row in the database. If someone runs a query against sensitive HR data at 2 AM, the log shows the same generic account that ran the payroll report at 9 AM. You cannot prove who touched what, and you cannot prove who didn't.
That ambiguity creates real legal exposure. If an employee asks "Is this not cybercrime and illegal surveillance?" after finding their private records accessed, the company has no defense. The shared login makes it technically impossible to distinguish between authorized access and unauthorized snooping. One person's curiosity looks identical to another person's job function.
Here's what that looks like in practice. Most audit systems log the authenticated principal, the resource accessed, and a timestamp. With individual credentials, you get clean attribution:
audit_log = {
    "timestamp": "2024-01-15T14:32:11Z",
    "user_id": "alice.chen@company.com",  # Unique identifier
    "action": "query",
    "resource": "employee_salary_table",
    "ip_address": "10.0.4.22"
}
But when everyone uses team-account@company.com, the log becomes useless for forensics:
Inside Flock's Surveillance Network
What changes when you move from a handful of cameras on a pole to a network spanning thousands of jurisdictions isn't just scale—it's the creation of a searchable memory. A single license plate reader tells you who drove past a specific intersection at 2 PM. The network tells you that the same car was three counties over yesterday, and the day before that, and where it parked for six hours at a time. That temporal stitching turns surveillance from an incident response tool into something closer to persistent tracking, and the legal frameworks most police departments operate under weren't built for that kind of longitudinal data.
I think the more unsettling part isn't the cameras—it's the business model underneath them. Flock isn't just selling hardware; they're selling access to a shared data commons where one department's footage becomes queryable by another, often without the driver's knowledge or meaningful oversight. This creates a privatized surveillance infrastructure that operates in the gaps between municipal budgets and state privacy laws. When a company profits from the aggregation of movement data across hundreds of agencies, the incentive structure shifts. The question becomes less about solving crimes and more about maintaining a subscription service that gets more valuable as more departments join.
What I'm watching for is whether this network effect survives legal pressure, or if it fragments the moment a court rules that warrantless cross-jurisdictional queries violate the Fourth Amendment. Right now, the system works because nobody has tested the boundaries—police treat the data like public record, while Flock treats it like proprietary software. That tension is sustainable until it isn't. The first major ruling that forces a choice between data retention and constitutional limits will tell us whether this is a durable infrastructure play or just a temporary arbitrage on privacy law.
The Local-to-Federal Data Pipeline
What's actually different here isn't the plumbing—it's the acceptance of eventual consistency as a design constraint. When you're pushing telemetry, user data, or operational metrics from local nodes (edge devices, on-prem clusters, developer workstations) into federal aggregation layers, you're signing up for a specific kind of drift. Local state is messy. It's partial, it's cached, it's sometimes wrong. I think most teams underestimate how much reconciliation work lives in that gap between "local truth" and "federal record." The pipeline becomes a translation layer, and translation always loses something.
The friction shows up in compliance overhead more than latency, at least initially. Federal systems trigger audit requirements, encryption standards, data residency rules that local dev environments simply don't have. Suddenly your local-to-federal pipeline isn't just moving bytes; it's enforcing policy. That means the people building this have to care about schema evolution across jurisdictions, retention policies, and access controls that vary by region. It's the kind of complexity that doesn't show up in architecture diagrams but does show up in on-call rotations at 2 AM.
I'm not sure we've figured out whether this hybrid model scales better than just keeping everything local until it's needed, or whether the federal layer becomes a bottleneck that forces teams to build increasingly elaborate local caches. The question worth sitting with: are we solving a data gravity problem, or are we just building a more expensive version of the same silos we already have?
Conclusion
Harpe is fired, but the infrastructure that let her husband run hundreds of warrant checks through a local police database hasn't changed. Flock still markets the same value proposition: pool your plate data across jurisdictions, get better results. The difference now is we know that "shared access" can include handing your credentials to a spouse who works for ICE.
The husband told investigators every search was tied to active federal warrants. That may be true. But Flock's audit trails record that a query occurred, not whether the warrant was legitimate or the target was correctly identified. When accountability depends on shared logins and self-reported justification, the vulnerability isn't really the unauthorized password—it's a system that treats every authenticated user as inherently trustworthy.
The next shared credential is already in use somewhere. The only question is whether that department has the documents to prove it.